Are Smart Glasses Banned in Europe? AI, Privacy and Trust
admin
||
October 29, 2026
Just because a technology can be used does not mean every use of it is lawful or socially acceptable.
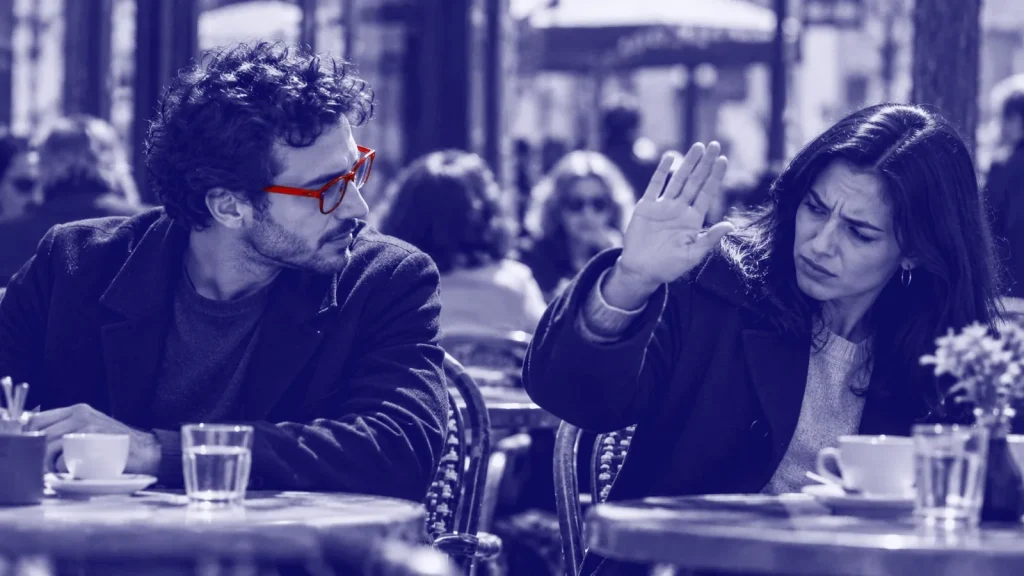
Do glasses only see what their wearer sees?
Imagine you are sitting in a café. The person at the next table is wearing what look like ordinary glasses. The glasses can record their surroundings, process the sounds they hear and pull information from an AI assistant. For the wearer, this is a practical convenience. But what does it mean for the other people who end up in the footage without wanting to? What choice does someone have if they don’t even notice they are being recorded?
AI-powered smart glasses are not just a new consumer electronics category. They sit on a boundary where technological function meets public space, consent, visibility and data protection. That is why the question “Are they banned in Europe?” is not enough on its own.
Is there an EU-wide ban on smart glasses?
As of 29 October 2026, there is no general EU-wide regulation that bans smart glasses outright as a device category. That does not mean every feature of these devices can be used freely everywhere either. What data the device collects, where it is used, who processes the data and for what purpose can all be decisive.
With Statement 1/2026, dated 13 October 2026, the European Data Protection Board (EDPB) highlighted the data protection challenges that smart glasses create. This statement is not, by itself, a new law banning all devices. Likewise, warnings from national authorities, the policies of specific venues and individual debates about bans should not be confused with an EU-wide product ban.
Why is GDPR part of the conversation?
The General Data Protection Regulation (GDPR) governs the processing of personal data under certain conditions. A person’s recognisable image, voice or information that makes them identifiable can count as personal data. Because smart glasses can record their surroundings continuously or unnoticed, they raise questions about why data is collected, whether it is necessary, how long it is kept and whether the people concerned are informed.
It would also be misleading to say every use falls under the same legal regime. There are exceptions and limits to GDPR’s scope for purely personal or household activities, but how they apply depends on the specific circumstances. How data responsibility is shared between the glasses manufacturer, the app provider, an employer and the individual user can also vary by use case. So generalisations like “the device exists, so recording is allowed” or “there’s a camera, so all recording is banned” don’t explain the legal picture.
What does the AI Act ban, and what does it regulate?
The EU Artificial Intelligence Act (AI Act) focuses largely on how AI systems are used and the risks they pose, not on what a device looks like. Some manipulative practices and certain forms of biometric use may be prohibited or tightly restricted. But not every AI function in smart glasses is automatically “prohibited biometrics”.
For example, showing a user directions and remotely identifying people in a crowd create very different data processing and risk profiles. Capturing a face on camera and biometric processing aimed at uniquely identifying a person are also separate concepts. A legal assessment has to consider purpose, context, the parties involved and the technical processes together. For a specific product or campaign, current legislation should be reviewed with a legal expert.
Why does the risk increase in workplaces, hospitals and schools?
These settings carry extra sensitivities: patient privacy in a hospital; child protection in a school; employee monitoring and power imbalances at work; the confidentiality of trade secrets in a meeting room. The same recording technology does not have the same social consequences on a street and in a medical consultation. Being technically “able to record” is not a valid reason for using it in every setting.
In these spaces, the organisation’s clear communication matters as much as users’ habits: Where is recording not allowed? How does the recording indicator work? Who can access the data? How is footage recorded by mistake deleted? Small decisions in technology design can affect how safe people feel.
For brands, this is about more than compliance
Privacy is not just a checklist for the legal department; it is part of the product experience and of brand trust. Making sure others can tell when the glasses are recording, limiting data collection to what is necessary, giving users clear controls and describing the product’s real capabilities without exaggeration are all strategic communication decisions.
The easiest route for a company marketing a new technology is to say “the future is here”. The more responsible route is to acknowledge the new power dynamics that technology creates. The impact that features designed to make users’ lives easier have on the choices of people around them should also be part of the story. A brand that inspires trust is not just one that offers innovation, but one that can talk openly about its limits.
Conclusion: The invisible design of innovation
The social acceptance of smart glasses won’t be decided only by camera resolution, battery life or how smart the assistant is. Who sees what, whose data is processed, how visible the notice is and how the options to object are designed will matter too. Good product strategy doesn’t separate ease of use from responsibility for privacy.
The debate in Europe can’t be explained as a categorical rejection of the technology. The more productive question is this: As smart devices become part of people’s lives, how can they protect the rights and trust of the people around them? This article reflects the regulatory picture as of 29 October 2026 and does not constitute legal advice.
References and further reading
- EDPB — Statement 1/2026 on smart glasses, 13 October 2026
https://www.edpb.europa.eu/documents/statement/statement-of-the-edpb-on-smart-glasses_en - CNIL — Smart glasses: calls for vigilance
https://cnil.fr/en/smart-glasses-cnil-calls-vigilance - European Commission — Navigating the AI Act
https://digital-strategy.ec.europa.eu/en/faqs/navigating-ai-act - AI Act Service Desk — Article 5
https://ai-act-service-desk.ec.europa.eu/en/ai-act/article-5
CATEGORIES